
Who Gives A Crap Customers Affected by Cyber Security Incident Involving Third-Party Provider
Australian toilet paper company Who Gives A Crap has notified customers of a cyber security incident involving a US-based marketing software provider, after unauthorised access to systems containing personal customer information was detected.
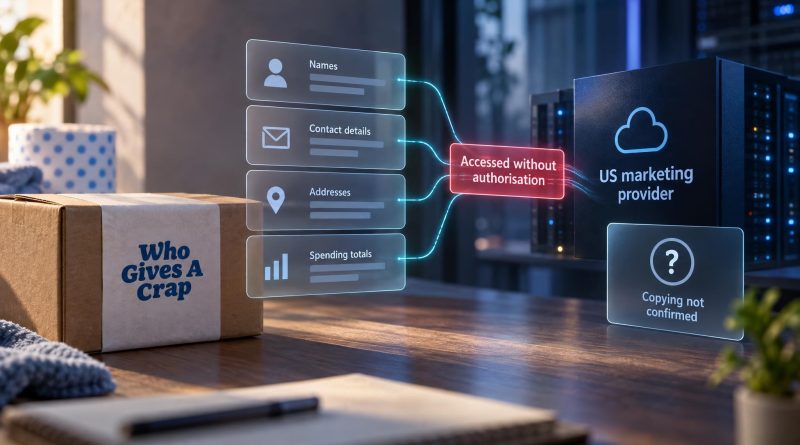
The incident potentially exposed customer names, contact details, residential addresses and spending information, although the company has emphasised that it remains unclear whether any personal data was copied or downloaded.
According to reporting by ABC News, the unauthorised access occurred within the systems of an external marketing provider responsible for storing customer information associated with Who Gives A Crap’s online shopfront.
The company has not publicly identified the affected provider or disclosed how many customers may have been impacted.
While the incident has raised concerns about the security of customer information shared with external technology suppliers, there is currently no confirmed evidence that the accessed data has been misused.
Customer Information Potentially Exposed
Who Gives A Crap confirmed that the information involved in the incident included customers’ first and last names, email addresses, phone numbers, mailing addresses and total spending amounts.
The company said payment information, individual order details and account passwords were not involved.
It also reassured customers that their Who Gives A Crap accounts had not been directly accessed and remained secure.
However, those assurances relate specifically to the company’s customer accounts and the categories of information it believes were affected. The unauthorised access occurred within the separate systems operated by its marketing software provider.
According to ABC News, customers in Australia, the United Kingdom and the United States were among those affected.
The external provider reportedly confirmed that personal information belonging to Canadian customers had not been accessed.
The company has not published a detailed breakdown of affected customers by country or provided an overall figure for the number of individuals whose records were accessible.
Importantly, the investigation has not established whether the information was viewed, copied, downloaded or subsequently transferred outside the provider’s systems.
That distinction remains central to determining the incident’s potential consequences.
Timeline of the Security Incident
According to Who Gives A Crap, the unauthorised access began on 30 October 2026.
The activity was reportedly detected the following day, 31 October, and access to the affected systems was secured by 1 November.
However, published accounts differ regarding when the company was informed and when customers received notifications.
ABC News reported that Who Gives A Crap was notified of the incident on a Friday, subsequently issued a public statement on Saturday and emailed affected customers that same day.
The Nightly, meanwhile, reported that customer notifications were distributed on Friday.
SmartCompany separately reported that the business was informed on 6 November, approximately six days after its provider detected the unauthorised activity.
These accounts establish a general sequence of detection, containment and customer communication, but they do not provide a fully consistent notification timeline.
The discrepancies do not, by themselves, establish that the company failed to meet any reporting obligations.
A clearer understanding of when the provider identified the affected records, when Who Gives A Crap received sufficient information to assess the incident and when customers were formally notified would be required to evaluate the response.
Who Gives A Crap has indicated that it will provide further updates if its investigation identifies additional information relevant to affected customers.
Third-Party Data Security Under Scrutiny
The incident has renewed attention on the risks associated with businesses transferring customer information to external technology providers.
Marketing platforms frequently hold personal information used to manage customer relationships, promotional communications and purchasing behaviour.
Although these arrangements can support business operations, they also create additional environments in which customer data must be protected.
A security failure affecting an external provider can consequently expose information belonging to customers of several businesses, even when the businesses’ own systems have not been directly compromised.
In this case, Who Gives A Crap said the affected information was held by a US-based marketing software provider supporting its online retail operations.
The company has not explained why the provider required access to all the categories of information involved, including physical addresses, phone numbers and cumulative customer spending.
Cyber security expert Troy Hunt, founder of the data breach notification service Have I Been Pwned, questioned the extent of customer information shared with external marketing providers.
Speaking to SmartCompany, Hunt argued that businesses retain responsibility for protecting information entrusted to them, even when that information is processed or stored by an external supplier.
He also raised concerns about whether marketing services require access to extensive customer records and suggested that limiting the information shared with third parties could reduce the consequences of future incidents.
His comments reflect broader concerns about data minimisation, a security principle under which organisations collect, share and retain only the personal information necessary for a legitimate business purpose.
Reducing the amount of information available to external suppliers can limit the potential exposure if those systems are compromised.
However, the available reporting does not establish whether Who Gives A Crap’s existing arrangements breached any legal requirements or recognised security standards.
Those questions would require further information about the provider’s services, data-handling arrangements and contractual responsibilities.
Company Disconnects Affected Provider
Following notification of the incident, Who Gives A Crap said it had taken steps to limit further access to its systems.
The company disconnected the affected marketing provider and changed relevant access credentials.
It also began communicating with the supplier to understand the circumstances surrounding the unauthorised activity and determine whether additional protective measures were required.
Chief executive and co-founder Simon Griffiths apologised to affected customers and said the business was continuing to monitor the situation while strengthening its cyber security protections.
The company also indicated that it would engage relevant regulatory authorities where required.
However, the published reports do not identify a formal regulatory notification or confirm that a government investigation has commenced.
There has also been no public explanation of how the unauthorised access occurred.
The provider has not been named, and no specific software vulnerability, compromised credential or other technical cause has been established in the available reporting.
Consequently, it remains unclear whether the incident resulted from a failure within the provider’s infrastructure, unauthorised use of legitimate access permissions or another form of compromise.
The available information also does not establish whether other businesses using the same provider were affected.
Customers Warned About Potential Scams
Although Who Gives A Crap said it had not identified evidence of customer information being misused, it urged customers to remain vigilant for suspicious communications.
Personal information such as names, contact details and residential addresses can be used by cybercriminals to make fraudulent messages appear more convincing.
Spending information may provide an additional means of tailoring scams to individual customers.
For example, a fraudulent email or text message could impersonate a familiar retailer and refer to genuine personal details to encourage a recipient to click a malicious link, provide additional information or make a payment.
Such techniques are commonly associated with phishing and social engineering attacks.
However, there is no confirmed evidence in the available reporting that customer information accessed during this incident has been used for those purposes.
Who Gives A Crap has advised customers to exercise caution when receiving unexpected emails, text messages, telephone calls or letters claiming to represent the business.
Customers have been encouraged to verify suspicious communications through the company’s official channels rather than relying on contact details or links supplied in unsolicited messages.
Those concerned about identity theft or fraudulent activity have also been directed to IDCARE, Australia’s specialist identity and cyber support service.
Suspected scams can be reported to the Australian Competition and Consumer Commission’s Scamwatch service.
While the company has stated that payment details and passwords were not involved, customers should remain cautious about unexpected requests for financial information or account credentials.
Data Access Does Not Necessarily Mean Data Theft
A significant unresolved issue is whether the unauthorised access resulted in customer information being removed from the provider’s systems.
Cyber security incidents can involve several different forms of exposure.
An unauthorised party may gain access to a database or account without necessarily downloading its contents.
In other circumstances, information may be copied or transferred to external systems, creating a risk that it could subsequently be distributed, sold or used for fraudulent activity.
Establishing which occurred requires technical evidence, including system logs, access records and findings from the provider’s investigation.
Who Gives A Crap has confirmed unauthorised access but has not established whether the affected information was extracted.
Similarly, the absence of identified misuse at this stage does not conclusively establish that the information was not copied.
These uncertainties limit any definitive assessment of the incident’s severity or its potential longer-term consequences for customers.
Broader Questions About Customer Data Protection
The incident highlights an increasingly important challenge for businesses that depend on external software providers to manage customer information.
Even when an organisation maintains appropriate protections for its own systems, information shared with third parties can be exposed through vulnerabilities or security failures elsewhere in its technology supply chain.
This makes supplier assessment, access controls, data minimisation and retention policies important components of an organisation’s broader cyber security responsibilities.
For Who Gives A Crap, the immediate priority remains determining the extent of the unauthorised access and whether customer information was copied or removed.
The company must also establish what caused the incident, whether further containment measures are necessary and whether any additional customer or regulatory notifications are required.
The number of affected customers and the final findings of the provider’s investigation remain undisclosed.
For customers, the immediate risk is the possibility that personal information could be used to support convincing fraudulent communications, even though no such misuse has been confirmed.
The case also raises a wider question about how much personal information retailers should share with marketing technology suppliers and how long those suppliers should retain it.
For now, Who Gives A Crap has reported that the unauthorised access has been secured, its customer accounts remain protected and there is no evidence of subsequent misuse.
The central question remains whether the information was simply accessed or also copied and removed.
Until the investigation provides a clearer answer, the full consequences of the incident cannot be established.
One question outlasts the copying uncertainty in this story: which customer details need to leave an online shopfront at all? Names, contact details and spending totals can serve marketing, but every extra field shared with a supplier widens the set of records someone else must protect. The broader groundwork of cybersecurity fundamentals helps you read that problem through systems, identities, access and defensive responsibility, rather than treating supplier risk as a single yes or no. That base makes it easier to ask what is held, who can reach it and what evidence would show a problem. If you want to build that understanding, The Hack Academy’s online cybersecurity training programme lists cybersecurity fundamentals among its subject areas, with self-paced learning and practical exercises alongside the theory in authorised, controlled environments.