
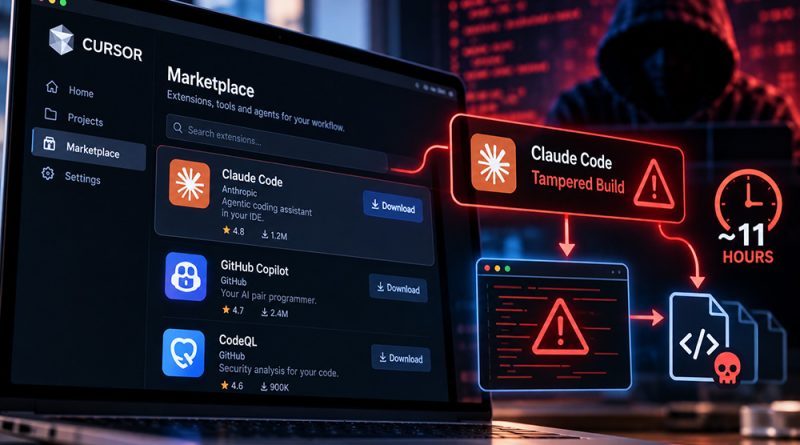
Cursor Marketplace Served Tampered Claude Code Builds for About 11 Hours
Cursor’s extension marketplace served tampered builds of Anthropic’s Claude Code extension for about 11 hours on 29 October 2026, according to Cursor’s security notice as reported by The Next Web, The Register and other outlets. The builds appeared under the legitimate identifier anthropic.claude-code, a detail that matters more than the familiar supply-chain label: the package looked like the real extension, arrived through the editor’s own marketplace and did not rely on a vulnerability in Claude Code.
Cursor’s revised notice, reported by The Hacker News, lists versions 2.1.312 and 2.1.313 for Windows and macOS. An earlier notice listed only 2.1.313. The malicious builds were available from approximately 02:27 to 13:35 Pacific Time, roughly 09:27 to 20:35 UTC. Cursor initially estimated that at most 5,000 users were affected and said it would contact them; its revised notice no longer states a user count. That figure is an initial estimate, not a confirmed total.
Early coverage placed the bad build on Open VSX. Later reporting by Field Effect and The Hacker News traced the distribution to Cursor’s marketplace only. Microsoft said the malicious version was never published or distributed from its Visual Studio Marketplace or through npm, and Cloud Security Alliance Labs, drawing on registry checks, reported that the 2.1.312 build on Open VSX was clean and that Open VSX had no 2.1.313 release. The correction matters for scoping: the relevant question is which marketplace supplied the extension, not which version string appears on disk.
Anthropic said, in statements reported by The Register, that the incident did not involve a compromise of its systems or employee laptops and that versions on its official channels were unaffected. That is a company statement, not independent confirmation. Neither Cursor nor Anthropic had publicly explained how the attacker obtained the ability to publish under Anthropic’s identifier or how the tampered build passed marketplace checks. Whether the build carried a cryptographic signature is unresolved.
Why the usual trust signals did not separate it
The build retained Anthropic’s extension identifier and publisher identity and followed the expected version sequence rather than using a lookalike name. For a developer, those are normally useful signals. Cursor extensions update automatically by default, so users with auto-update enabled could have received the build without taking action, according to The Hacker News, citing Phorion and OpenSourceMalware. The 11-hour exposure window, rather than a user’s decision to install something suspicious, became the relevant control point.
Cloud Security Alliance Labs has suggested that a team-level install cooldown longer than the exposure window would likely have kept hosts from receiving this build. The analysis calls that an inference, the setting is disabled by default, and its effectiveness against this specific artefact has not been tested. Cloud Security Alliance Labs adds that allowlisting approved publishers or extension IDs would not have blocked a build using the legitimate identifier, although it would narrow the pool of extensions that could be abused. Cursor’s option to require valid Open VSX signatures might have blocked this build because 2.1.313 was never published there, but neither vendor has confirmed that behaviour, and the analysis recommends testing it rather than assuming it.
What the payload did, and where it failed
Dark Reading, citing OpenSourceMalware, described a 66-line loader inserted before the legitimate code in extension.js. It ran when the extension loaded, without requiring a Claude conversation or further user action. It collected the hostname, username, operating system and architecture, home and working directories, configured Git email, public IP address, and the names of up to 40 environment variables associated with credentials and cloud services. The values of those variables were not reported as collected.
The loader added an attacker-controlled SSH key labelled svc-telemetry to the user’s authorized_keys, attempted to enable the local SSH service and a reverse SSH tunnel, installed platform-specific persistence, and sent host reconnaissance over HTTP.
Cursor said that enabling the local SSH service required administrator rights the extension lacked on most macOS and Windows hosts, so that step usually failed there. The key, the persistence and the data upload still occurred. No successful use of the reverse tunnel or follow-on activity has been publicly confirmed. Reporting has described Linux persistence logic, but no Linux build was reported as distributed; the affected Cursor marketplace builds were for Windows and macOS. Cloud Security Alliance Labs noted that a macOS host with Remote Login already enabled could have been exposed by the planted key alone. That is an inference rather than a confirmed compromise, and the number of such hosts is unknown.
The incident is a distribution-layer compromise, not a vulnerability in Claude Code. The AI-specific element is the host. As Field Effect notes, extensions run with the permissions of the signed-in user and can reach source code repositories, development tools, cloud credentials and authentication tokens. Coding extensions are installed widely, updated often and granted broad local authority because that authority makes them useful. None of that makes the payload a novel exploit. Reporting describes a conventional backdoor delivered through a software supply chain, and the public record offers no basis for ranking this incident against other developer-tool attacks.
Cursor said it removed the malicious builds, took its marketplace offline while it checked other extensions, rotated its keys, restored the marketplace, worked with the hosting provider to take the attacker’s server offline and published scripts to check for and remove the backdoor. Those are vendor statements and have not been independently verified.
Cleanup is separate from updating
Cursor identified 2.1.314 as the clean version to install, but updating or uninstalling the extension does not remove an SSH key or persistence already written to disk. Version 2.1.314 is a replacement, not a removal tool, and its release notes do not describe a security patch. Advice from Cloud Security Alliance Labs, Field Effect and Microsoft is to identify hosts that installed or updated the extension from Cursor’s marketplace during the window, preserve evidence, isolate the host, remove unauthorised SSH keys, persistence and tunnel processes, review endpoint and network telemetry, and rotate credentials and revoke sessions from a trusted machine. A host whose tunnel is known to have connected should be considered for rebuild rather than cleaning.
Neither company had explained the publication path. The public record does not establish whether any tunnel session was used, whether follow-on access occurred, or who was responsible. The exact number of affected users is also unresolved after Cursor removed its initial estimate from the revised notice. Those gaps do not prevent teams from scoping exposure by marketplace, time window and host artefacts, but they do prevent a definitive account of which marketplace control failed.
For responders, the useful distinction is between a clean extension and a clean host. Installing 2.1.314 addresses the first. Only investigation, removal of the planted access and rotation of reachable credentials address the second.
An update replaces the code that runs; it does not reach into an SSH configuration and withdraw a key already written there. Holding those two kinds of damage apart, the artefact left on a machine and the action it may or may not have taken, is the quieter half of security work and a skill rather than a checklist. Cybersecurity fundamentals treats evidence, scope and permission as things to establish: which hosts met which condition, what the record actually shows, and where an inference has quietly become an assumption. That discipline is what turns an exposure window of about 11 hours into a defensible list of machines to examine rather than a guess. Readers who want to build it can explore The Hack Academy’s online cybersecurity training programme, whose subject areas include cybersecurity fundamentals, with self-paced learning and practical exercises alongside the theory.