
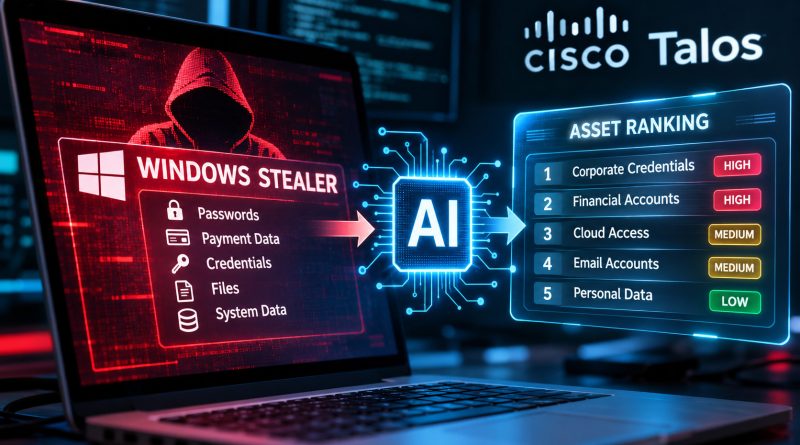
Cisco Talos documents a Windows stealer designed to let an AI model rank stolen assets
Cisco Talos has published technical research on VOLTA, a Windows infostealer that can send a structured bundle of stolen data to a large language model (LLM) for an assessment of the victim’s assets. The research documents a design, not a confirmed campaign. Talos describes the AI stage as optional, and no public victim count or confirmed infection has been reported. Nor does the reporting show a model that complied with the request.
The report separates designed capability from observed operation. The model is not described as breaking in or choosing exploits; it reads stolen material and produces an assessment. That makes it a triage layer for data already taken, not an autonomous intruder.
A broad theft pass, then enrichment
Talos’s collection list is wide but specific. It includes browser passwords and cookies, payment cards, cryptocurrency wallet seed phrases, sessions for Discord, Telegram, Steam and Roblox, Microsoft OAuth tokens, SSH and cloud provider keys, Wi-Fi profiles and screenshots. That supports the description of a mature stealer with a large reach. It does not support the idea that the malware takes everything on a machine.
The second stage turns a credential log into a profile. Talos says VOLTA builds a structured evidence bundle containing geolocation, home address, employer and employer domain, an inferred birth year, the last four digits of payment cards, Slack workspaces, document authorship metadata, iPhone backup indicators and a Roblox account valuation. It then uses stolen session access to search the victim’s Gmail for purchase receipts to corroborate a home address, pull UberEats and DoorDash order history, and enrich Discord accounts through the stolen token.
This enrichment is designed behaviour. It shows how ordinary account access can be combined into a fuller picture of a person, and it explains why the AI stage, if it runs, receives a dossier with identity, employer, spending and asset clues rather than a password list.
The model as a triage analyst
Talos reports that the bundle is serialised and sent to OpenRouter, a service that routes prompts to different model providers, under a system prompt that casts the model as a forensic intelligence analyst drafting a target assessment. The required output includes a ranking of valuables by monetisation, with low, medium and high tiers, and a section assessing the victim’s security posture and password hygiene.
The configuration uses a chain of models. The default model is Anthropic’s Claude Opus 4.6, with fallbacks to Moonshot AI’s Kimi K2 and Google’s Gemini 2.5 Flash. Talos says the request runs at a low temperature setting and that the malware checks responses for refusal language before moving to the next model. That design shows the authors expected refusals and built around them. It does not show that any model complied or that Anthropic, Moonshot AI or Google knew about the calls. The model names describe what the malware’s code is configured to call, not evidence of provider approval, and the reporting includes no comment from the three companies.
The model call follows collection and enrichment, so its role is to sort what was taken and judge its value, not to gain access. That is a narrower use of AI than the label AI malware can imply, but it is still meaningful: it places an analytical step that might otherwise require a person into an automated pipeline.
Designed, not demonstrated
The public evidence stops well short of an active campaign. TechRadar’s report notes that Talos did not say where the malware was found, how many devices it infected or how it is distributed. AI News Today, citing a Talos researcher via WIRED, says the team did not track in-the-wild use, so there is no public victim count. The research does not establish an infection vector, prevalence or operational scale. Brandefense’s summary notes that Talos does not attribute VOLTA to a named threat actor, criminal group or country. Those gaps are unknown, not zero. The absence of a victim count is not proof that no use occurred.
Talos describes the sample it examined as a 64-bit Windows executable first observed on 11 October 2026. The report says VOLTA is self-deleting and that all observed endpoints are third-party controlled, with no attacker-owned infrastructure. The first-seen date is not an infection date. Those details matter for investigation and attribution, but they do not settle how widely, if at all, the malware has been deployed.
A separate open question is the commercial model. Talos reports that VOLTA uses a template with six swappable slots filled at build time, including the Telegram channel for exfiltration, API keys and other settings. Talos assesses that this suggests a builder model in which a customer supplies values and receives a custom binary. That is an inference from the design; no customer, price or transaction is reported. It points to a possible builder arrangement, not a confirmed sale or known customer base.
What defenders can do, and what remains open
There is no patch or fixed version for VOLTA because the research concerns malware, not a disclosed software vulnerability. Talos’s defensive advice focuses on limiting credential and session theft and preserving forensic artefacts. It recommends application control over which processes may launch Chrome in headless mode, and alerts on unexpected headless launches. It also recommends hardware-backed credential stores where possible.
If a compromise is suspected, the guidance is to preserve the volta_debug.txt harvest log, revoke potentially compromised tokens, change passwords, and treat any cryptocurrency wallet whose seed phrase was stored in plain text as compromised. Funds should be moved to a new wallet with a seed generated on an air-gapped device. Because no infection vector is established, the advice cannot address initial access; it is mitigation and remediation guidance, not a patch.
Recorded Future’s Insikt Group said in December 2025, before the VOLTA reporting, that most AI malware observed so far sat at levels 1 to 3 of its AI malware maturity model and that AI was then a force multiplier on existing techniques, not a source of fundamentally new tactics. The assessment is general and predates this case, so it does not settle how well VOLTA’s model stage works.
The unresolved question is whether the assessment improves an attacker’s decisions enough to justify the extra configuration. Talos documents the mechanism, the model chain and the intended output. It does not show a real victim dossier or a success rate for the AI stage. The evidence supports a narrower description than the idea that the malware steals everything and ranks the victim’s worth: a designed post-theft triage layer, a broad collection capability and an unknown record in the wild.
A malware stage that dials through three different models, checking each reply for a refusal before moving to the next, reveals its authors’ expectations rather than any model’s behaviour. That gap between what a design anticipates and what has been shown to happen is familiar ground in security, where a control can be written into a policy or a configuration and still never be examined. Cybersecurity fundamentals treats stated safeguards as claims to scope, test and record, rather than settled facts. Readers who want to build that habit can explore The Hack Academy’s online cybersecurity training programme, which lists cybersecurity fundamentals among its subject areas and sets self-paced learning and practical exercises alongside the theory.