
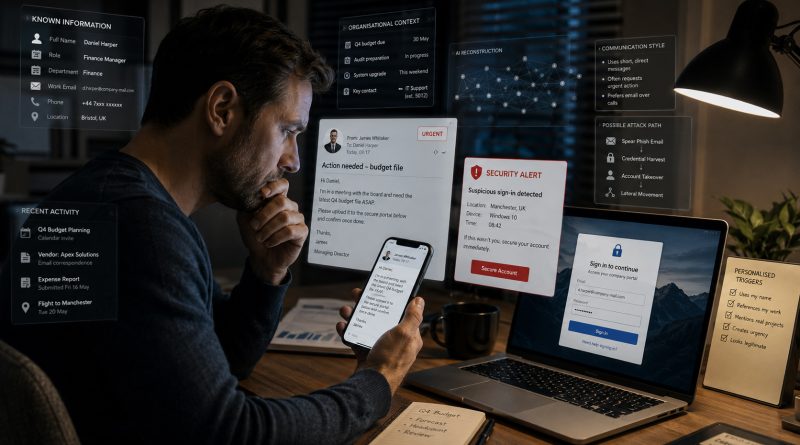
The scam that knows your name is coming
For years, online scams have relied on volume rather than sophistication. Send the same poorly written email to a million people, promise an impossible inheritance or threaten an overdue tax bill, and eventually someone will respond.
Artificial intelligence is about to make that model look primitive.
The next generation of scams will not be written for a crowd. They will be written specifically for you.
The attacker may know where you work, what your role involves, who your manager is, where you recently travelled, which supplier your company uses and what project is currently demanding your attention. The message may arrive at exactly the moment you are most likely to believe it.
It could appear to come from your chief executive asking you to urgently approve a payment. It might be a WhatsApp message from a colleague who claims to be locked out of an account. It could be an email from a real estate agent, accountant, school, pharmacy or government department that references genuine details about your life.
Nothing about it will immediately look unusual.
This is the threat posed by AI-powered spear phishing, a highly personalised form of deception designed around an individual target.
Traditional phishing attacks often reveal themselves through generic greetings, spelling mistakes, awkward phrasing and implausible requests. Spear phishing is different. It is researched, targeted and tailored to match the victim’s circumstances.
Until recently, creating that level of personalisation required time and effort. A criminal had to manually investigate a target, study their relationships, understand their workplace and maintain a believable conversation.
AI can now assist with much of that work.
A capable model can collect publicly available information, identify useful relationships, imitate a credible authority figure and generate messages that sound natural. It can also adapt when challenged.
Ask the supposed executive why they cannot process the payment themselves, and the system can produce a plausible explanation. Question why a colleague is messaging from a different number, and it can invent a believable story about a lost phone. Request verification, and it may attempt to redirect you towards another compromised account or fake website.
This is what makes the emerging threat so dangerous. The scam no longer needs to be perfect in its opening message. It can behave like a patient and persuasive human being.
The criminal operation behind it can potentially manage hundreds or thousands of individual conversations at once.
That changes the economics of fraud.
The reconnaissance, approach, persuasion and exploitation stages of a social engineering attack have traditionally required human involvement. AI agents could increasingly automate that entire sequence, allowing criminals to target more people with far greater precision.
The result will not simply be more scam emails. It will be believable relationships manufactured for the purpose of exploitation.
Businesses are particularly vulnerable because modern workplaces are built around speed and trust. Employees respond to messages while moving between meetings, travelling, serving customers or dealing with competing deadlines. They approve invoices, open shared documents and reset passwords as part of their ordinary working day.
Attackers do not need every employee to fall for the deception. They need one person to act before stopping to verify the request.
Many organisations already conduct phishing simulations and cybersecurity awareness training. That is valuable, but the familiar training exercise may soon be inadequate.
Employees are usually taught to look for obvious warning signs. Check the sender’s address. Watch for spelling mistakes. Be suspicious of generic greetings. Avoid unexpected links.
Those habits remain important, but AI can remove many of those clues.
The message may be grammatically flawless. The tone may resemble the person being impersonated. It may refer to a real meeting, a genuine transaction or an actual workplace problem. The attacker may know enough about internal processes to make the request feel routine.
Even experienced professionals can be deceived when a message is credible, urgent and personally relevant.
Research into the ability of AI models to complete longer and more complex tasks suggests the risk could escalate quickly. Some projections indicate that common business email compromise attacks may become fully automated from late 2026. More sophisticated fraud operations could potentially be automated from beginning to end during 2027.
Predictions about rapidly developing technology are never certain, but waiting for perfect certainty would be reckless.
Regulators and AI developers must begin treating financial deception as a major safety issue rather than a secondary misuse problem.
Much of the public discussion around advanced AI focuses on dramatic scenarios involving autonomous cyberattacks, biological weapons or systems escaping human control. Those risks deserve serious scrutiny, but they should not distract from harm that is already becoming practical.
An AI system does not need to discover an unknown software vulnerability if it can persuade an employee to reveal a password.
It does not need to break through a bank’s security systems if it can convince a customer to transfer the money voluntarily.
It does not need to impersonate someone perfectly. It only needs to sound convincing long enough for the victim to act.
AI companies should be required to test new models for their ability to conduct extended social engineering campaigns. Those evaluations should examine whether models can research targets, maintain false identities, overcome suspicion and guide victims towards harmful actions.
Governments should also ensure that fraud, impersonation and deception for financial gain are explicitly included in AI safety regulation.
But regulation alone will not protect individuals or businesses.
Organisations need verification procedures that do not depend solely on whether a message sounds authentic. Unexpected payment requests should be confirmed through a separate communication channel. Password resets and changes to banking details should require additional approval. Staff should be given the confidence to pause a transaction, even when the request appears to come from someone senior.
Businesses must also update their training. Employees need to understand that a scammer may already know the answers to basic identity questions. A familiar writing style, personal detail or convincing voice recording can no longer be treated as proof of identity.
The same caution applies at home.
A message that mentions your family, employer, recent purchase or travel plans may feel legitimate because the information is accurate. In reality, those details may have been collected from social media, data breaches, professional profiles and other public sources, then assembled by an AI system into a highly believable story.
The old advice was to avoid messages that looked suspicious.
The new advice is more uncomfortable. Be prepared to verify messages that look completely genuine.
The most dangerous scam of the AI era may not be the one filled with obvious mistakes. It may be the one that arrives at the right time, uses the right language and appears to understand your life.
Most of us have learned to recognise a message written for everyone.
Far fewer are ready for one written only for us.