
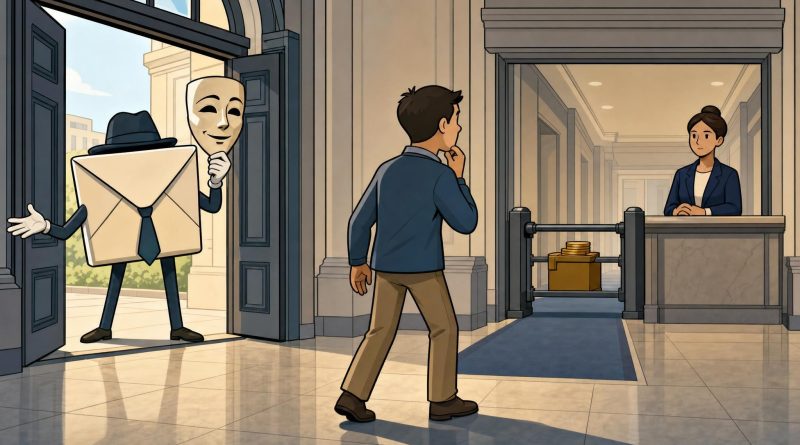
Spoofing is an identity design failure, not just a vigilance test
A 2024 article about spoofing resurfaced through a 2026 republication. HuffPost originally published the piece on 29 August 2024, according to Yahoo’s syndication and the National Cybersecurity Alliance. Yahoo Tech republished it on 27 September 2026. The republication was not a new scam event, but it is a useful prompt to examine a persistent problem: communications interfaces still encourage us to read appearance as identity.
The familiar response is to tell people to be more suspicious, treat unexpected contact cautiously and restart contact through a route chosen independently. That advice can help, but it leaves the recipient acting as the final authentication mechanism for interfaces designed to display names, numbers, logos and domains prominently. We should treat spoofing less as a recurring failure of individual vigilance and more as a failure to design identity, provenance and high-risk actions coherently.
A name is not proof
Spoofing is a convenient umbrella term, but it can obscure important technical differences. Falsified caller ID, misleading email presentation, lookalike domains and deceptive links are not one vulnerability. They operate through different channels and require different controls. What unites them is the gap between what an interface shows and what the recipient can safely infer from it.
A familiar caller name may suggest who is calling without proving it. The US Federal Communications Commission warns that caller ID information can be falsified and advises people not to rely on the displayed identity when an unexpected caller asks for personal information. The sensible immediate response is to end the contact and use a number obtained independently.
Email has a more developed set of domain authentication technologies, but their meaning is often overstated. RFC 7489 defines DMARC as a domain-level authentication, policy and reporting mechanism built around SPF and DKIM identifiers. NIST documents SPF, DKIM and DMARC together as email trust technologies and discusses their deployment by organisations.
These controls matter. DMARC can evaluate alignment between relevant identifiers and apply a domain’s policy. What it cannot do is establish that the message is truthful, that its request is legitimate or that the person composing it has good intentions. Technical provenance and human trustworthiness are different propositions. An email can satisfy domain authentication checks without earning confidence in every claim it contains.
This distinction should shape interface design. Platforms ought to translate useful machine-readable provenance into restrained, comprehensible signals rather than expecting ordinary recipients to interpret headers and protocol details. Yet a badge that merely says a message is authenticated could create another problem if people understand it as an endorsement. Any such signal must explain its narrow scope: it says something about provenance, not truth. This is a design proposal, not a proven intervention.
Infrastructure can narrow the deception
Australia’s SMS Sender ID Register offers a useful partial model. Guidance from the Australian Communications and Media Authority describes a register for alphanumeric sender identities and an Unverified treatment for sender IDs outside the scheme. That can make missing registration visible, which is better than presenting every branded sender name without distinction.
But the register should not be made to promise more than its scope allows. It concerns alphanumeric SMS sender identities. It does not authenticate voice calls, email, web addresses or every person operating behind a message. Nor does registration prove that the content of a message is safe. An Unverified label is a warning signal, while the absence of that warning cannot sensibly become a universal guarantee.
This is the general pattern across communications security. Channel-specific controls can establish limited facts about how a message arrived or how an identifier aligns. They cannot collapse provenance, content, intent and authority into a single trustworthy symbol. The goal should not be to find one perfect badge. It should be to combine better provenance with workflows that remain safe when presentation cues fail.
Verify the action, not just the message
The strongest defence is to attach verification to the requested action. A payment, account recovery or disclosure of sensitive information should not become valid merely because it began with a convincing call, email or text. Banks, employers and public agencies should provide independently reachable account channels or additional approval steps for consequential requests.
If an organisation maintains an authenticated dashboard that users can reach without following an inbound link, it can separate the message that creates attention from the channel that authorises action. If a second approval is required for a sensitive change, one persuasive message may become less capable of producing immediate harm. This is a design proposition, not a guaranteed outcome. It assumes that users retain access to the trusted route, and it does not remove the risk posed by a compromised authenticated account.
Organisations should also make pausing an expected part of the process. A customer or employee who receives an urgent request needs a safe way to stop, navigate independently and verify what is being asked. A workflow undermines its own security if it demands immediate compliance through an unsolicited channel while telling recipients elsewhere to distrust urgency.
This approach changes the measure of success. It is tempting to judge anti-scam systems by whether a person spots a fake. A better question is whether the fake, even when believed temporarily, can complete a harmful action. Detection remains valuable, but containment is more durable than assuming that every recipient will notice every inconsistency.
Friction is a feature when the stakes justify it
There are legitimate objections. People still need basic digital literacy because no authentication technology validates all content or covers every channel. Independently initiated callbacks and extra approvals also consume time. Applied indiscriminately, they could obstruct routine activity and make urgent legitimate work harder. Such friction can create usability and accessibility costs, although their scale is not established here.
That is an argument for proportionate friction, not for avoiding friction altogether. Routine messages need not carry the same burden as payments, account recovery or requests for sensitive data. The higher the consequence of a mistaken decision, the less an institution should depend on recognition of a familiar name or number. Organisations can choose where additional approval provides enough value to justify delay.
Users still have a practical role. When unexpected contact asks for money, credentials or personal information, leave the inbound channel. Navigate to a known service directly, use contact details obtained independently and do not treat a familiar display identity as proof. But this should be the fallback behaviour around a safer system, not an excuse for institutions to transfer the whole authentication burden to the person under pressure.
Spoofing remains useful to deceivers when interfaces compress uncertain evidence into confident presentation. The durable response is not to ask whether every message looks genuine. It is to ask whether the requested action would remain safe if the displayed identity were false. Platforms can clarify provenance, but banks, employers and agencies must ensure that appearance alone never carries the authority to move money, recover an account or disclose sensitive information.
Judging a message means separating what technical provenance can establish from what it cannot. The Hack Academy’s online cybersecurity training programme offers a practical next step, with self-paced learning in cybersecurity fundamentals and networking, plus practical exercises alongside theory.
