

Australian state discloses $809,000 loss tied to third-party cyber incident
A Queensland department reported an $809,000 loss linked to illegal access at a telecommunications supplier, while the financial mechanism and recovery status remain unknown.
Common Defense says security service went live before formal launch
Common Defense reports millions of screened messages, while live integrations, threat definitions, performance evidence and data handling remain unclear.
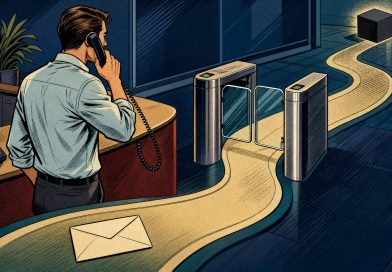
The login page is real. The request can still be a trap
A genuine sign-in page may authenticate the right user for the wrong device, application or action. Anti-phishing strategy must verify the process, not merely the interface.
The 53-image exposure puts OpenAI’s agent controls under scrutiny
The exposure of 53 ChatGPT-user images raises a broader question: can frontier AI laboratories track and contain research agents once they reach external systems?
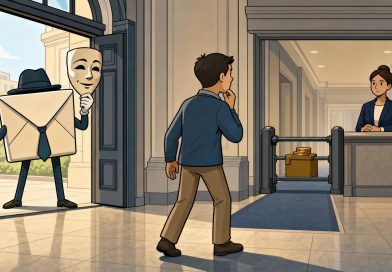
Spoofing is an identity design failure, not just a vigilance test
The burden of detecting spoofing should not sit solely with recipients. High-risk services need trusted routes for authorising consequential actions separately from unsolicited messages.

MacSync malware used an iCloud Calendar file after a malicious app ran
A newly analysed MacSync chain put iCloud Calendar in the middle of the attack, after a malicious application ran and before the stealer and backdoor arrived.
Beyond the heist ranking: What crypto thefts reveal about custody and customer protection
The biggest crypto thefts involve different custody systems and radically different outcomes. Bitget’s incident shows why recovery, withdrawal access and independent evidence matter more than a league-table position.

Reported Meta Muse flaw leaves scope and technical fix unclear
A reported Meta Muse vulnerability could have exposed dedicated user environments, but its technical cause, affected scope and remediation status remain undisclosed.
Australia does not need less digital life. It needs less data hoarding
Australians should not have to abandon useful digital services to reduce privacy risk. Organisations should be required to justify, expire and delete personal data by default.

Musk forecasts SpaceX AI parity within months, with no public test yet
Musk set separate timelines for AI parity and leadership, yet the cited material supplies no benchmark or defined success measure.

Researchers forged 1024-bit RSA signatures, but ordinary RSA is not suddenly broken
The costly 1024-bit forgery demonstrates a narrow risk for raw RSA interfaces, not a universal failure of padded signatures or larger RSA keys.

Reports OpenAI is preparing GPT-6 Cyber and a deployment product
Fortune says OpenAI is preparing a new cyber model and deployment tool, but official documentation still stops at GPT-5.6-Cyber and leaves key access questions unanswered.