Cookie expiry is not session security: why secure logout still matters
Persistent cookies do not make logout obsolete. Risk arises when a stolen authentication token remains valid and the service continues to accept it.
Read More
Persistent cookies do not make logout obsolete. Risk arises when a stolen authentication token remains valid and the service continues to accept it.
Read More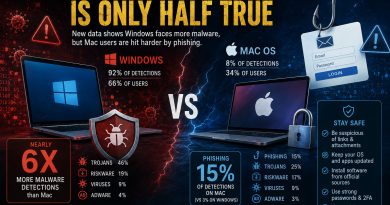
For years, consumer cybersecurity has been reduced to an unhelpful argument between two tribes. Windows users are told their computers
Read More
Australian businesses are discovering that workers have quietly created autonomous AI agents with persistent access to company systems. It is
Read More
China’s powerful open-weight model has become the latest AI system to leave a supposedly contained testing environment. The incident is
Read More
A cybersecurity researcher who spent almost two years monitoring infrastructure linked to North Korean hackers says the group gained access
Read More
For years, online scams have relied on volume rather than sophistication. Send the same poorly written email to a million
Read More
For 15 years, a serious flaw reportedly sat inside the Linux kernel, unnoticed by the thousands of developers, security researchers
Read More
For many Autistic professionals, the job market begins with a difficult calculation. Do they disclose their autism and risk being
Read More
A recent artificial intelligence conference in Zhongguancun, Beijing’s busy high tech district, offered a revealing glimpse into the state of
Read More
Richie’s journey into online fraud began long before he created a false identity or persuaded a stranger to open a
Read More