
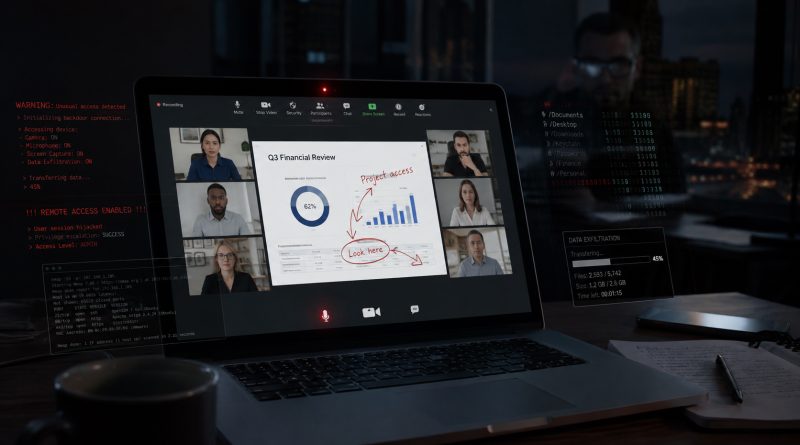
AI-assisted ‘Zoomsday’ flaw could have hijacked devices across entire meetings
Security researchers say they developed a working attack against Zoom in less than 24 hours, using fewer than 20 prompts submitted to publicly available artificial intelligence models.
Zoom has patched a series of serious vulnerabilities that could have allowed a malicious meeting participant to take control of another attendee’s device without requiring the victim to click a link, open a file or approve a download.
The vulnerability chain, dubbed ZOOMSDAY by researchers at cybersecurity firm A Security, was found within Zoom’s annotation system. This is the feature that allows participants to draw, type, highlight or place shapes over shared screens and digital whiteboards during a meeting.
Rather than transmitting annotations as simple images, Zoom converts them into structured data that is sent between meeting participants. The receiving Zoom application then automatically processes that information so the drawing or text can be recreated on screen.
Researchers discovered that specially crafted annotation data could corrupt the memory of the receiving application. In certain circumstances, this could allow an attacker to run their own code on another participant’s device.
No warning would appear on the screen and the victim would not need to be actively using the annotation feature. Their presence in the meeting could be enough to expose them to the attack.
The position of the attacker within the meeting affected who could be targeted. A malicious participant could direct an attack towards the person sharing their screen, while a compromised presenter could potentially target multiple people watching the presentation.
Once malicious code was running, an attacker could attempt to steal personal or business information, install additional malware, or access permissions already granted to Zoom, including the device’s camera and microphone. The flaw was confirmed across Zoom’s native clients on major operating systems, including Windows, macOS, Linux, Android and iOS.
What makes the discovery particularly significant is the speed at which the researchers say they moved from identifying the weakness to building a working exploit.
According to A Security, the process took less than one working day and involved fewer than 20 prompts submitted to publicly available AI models. The company argues that comparable research would previously have required a highly specialised team, substantial resources and months of work.
The technical disclosure shows that experienced human direction and specialist security tools were still involved. Researchers decompiled Zoom’s Android application, traced communication between clients, mapped the platform’s proprietary annotation protocol and directed the AI systems towards potentially dangerous areas of code.
The AI did not simply produce a complete attack from a single request. Instead, it appears to have dramatically accelerated the analysis, reverse engineering and exploit development process. This distinction is important, but it does little to reduce the broader concern. AI is lowering the time and cost required to investigate complicated software, and those capabilities can be used by defenders and attackers alike.
The disclosure involves three vulnerabilities tracked as CVE-2026-53413, CVE-2026-53414 and CVE-2026-53415.
Zoom classified the first vulnerability, a buffer overwrite, as high severity with a score of 8.3 out of 10. The company said it could allow one meeting participant to achieve remote code execution on another participant’s device.
The second vulnerability involved a buffer over-read and was classified by Zoom as medium severity, with a score of 6.5. Zoom said it could be used to cause another participant’s application to crash or become unavailable.
The third was a use-after-free vulnerability, also rated high severity with a score of 8.3, which could provide another path towards remote code execution.
A Security identified the initial annotation vulnerability on 8 June 2026 and confirmed a working attack against Zoom Client version 7.0.5 the following day. The company reported its findings to Zoom on 10 June.
Zoom released client-side fixes for the first two vulnerabilities in version 7.1.0 on 22 June and introduced a server-side mitigation on 15 July to provide additional protection for users who had not yet updated. A further client-side fix addressing the third vulnerability was released in version 7.1.5 on 20 July. The vulnerabilities were publicly disclosed on 11 August 2026.
Zoom has advised customers to install the latest available versions of its software. The affected products include Zoom Workplace across supported platforms, the Zoom Workplace VDI Client for Windows, Zoom Rooms and the Zoom Meeting SDK.
Users should update Zoom on every computer, phone and tablet they use, even when the application appears to be working normally. Organisations should also confirm that centrally managed devices are receiving current versions rather than relying entirely on individual employees to perform updates.
Meeting hosts can further reduce their exposure by using passcodes, waiting rooms and authenticated participant requirements. Screen sharing and annotation access should be restricted when they are not required, particularly during meetings involving external attendees or publicly distributed invitation links.
The ZOOMSDAY discovery demonstrates why familiar platforms and trusted meeting invitations should never be treated as automatically safe. Software updates remain essential, but effective protection also depends on people understanding how cyber threats operate and knowing how to recognise suspicious behaviour before serious damage is done.
Improve your ability to protect yourself, your information and your organisation by taking The Hack Academy’s Online Training Programme. Build practical cybersecurity knowledge, strengthen your everyday security habits and become a harder target for cybercriminals before the next major vulnerability reaches the headlines.