Inside the 17.9 billion-record tally: the limits of megabreach league tables
The 17.9 billion record figure describes a curated collection of large reported events, not unique victims or a definitive ranking of sector breach risk.
Read More
The 17.9 billion record figure describes a curated collection of large reported events, not unique victims or a definitive ranking of sector breach risk.
Read More
Affected self-managed GitLab CE and EE installations require branch-specific upgrades after CISA confirmed exploitation of CVE-2026-85706.
Read More
Brevo says a SAML SSO authorisation failure exposed 138 client accounts, including abuse of Trezor’s newsletter channel to send phishing to roughly 347,000 addresses.
Read More
CISA has confirmed exploitation of CVE-2026-53362. Linux and container operators should verify their distribution’s kernel fix rather than rely on upstream version numbers alone.
Read More
Microsoft’s September updates address two exploited Windows privilege-escalation flaws, which should take priority over the release’s disputed headline totals.
Read More
Berlin tightened safeguards after an additional package of stolen state administration data containing credentials was published, as officials continued reviewing files and assessing who must be notified.
Read More
MAG has confirmed customer-data theft across three airports, while outlets report an online release and independent research supports exposed API credentials as a plausible access route.
Read More
JLR’s two-year plan targets approximately 4,000 roles, but its records do not support claims that the 2025 cyber incident was the sole cause.
Read More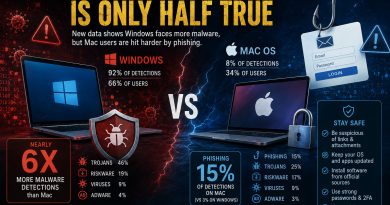
For years, consumer cybersecurity has been reduced to an unhelpful argument between two tribes. Windows users are told their computers
Read More
Cyber security teams intercepted sophisticated attempts to infiltrate aviation, energy and education systems before services or data were compromised. The
Read More