Why cheaper AI models can still produce bigger bills
Cheaper model queries do not guarantee smaller AI bills. Organisations need to measure complete costs, production quality and governance against successful outcomes.
Read More
Cheaper model queries do not guarantee smaller AI bills. Organisations need to measure complete costs, production quality and governance against successful outcomes.
Read More
Security automation should be measured not only by speed and savings, but by whether it reduces concurrent work, interruptions and decision pressure for incident responders.
Read More
Attack-path analysis can expose high-leverage security chokepoints, but its value depends on accurate graphs, controlled remediation and strict limits on agent authority.
Read More
AI is shrinking the tolerance for old software and slow remediation. The advantage will go to institutions that can turn faster discovery into safe, reversible change.
Read More
Global cyber surveys can focus executive attention, but organisations still need to rank risks by local consequences, dependencies, ownership and tested recovery.
Read More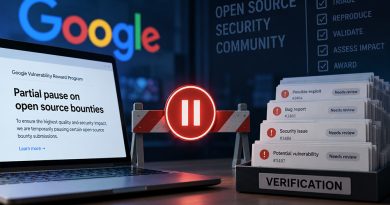
Google’s limited OSS bounty pause shows why reproducible evidence and demonstrated impact, rather than AI use alone, are becoming central to vulnerability-report triage.
Read More
One engineer’s route into Google security shows how software skills, documented security work, education and exceptional access combine in a career pivot.
Read More
The enduring principles of cybersecurity still matter, but AI demands faster execution, task-scoped agent authority and recovery plans that work in practice.
Read More
Frontier cyber tools should be judged by remediation, affordability and downstream protection, not vulnerability counts or partner prestige.
Read More
A genuine sign-in page may authenticate the right user for the wrong device, application or action. Anti-phishing strategy must verify the process, not merely the interface.
Read More