
US state cyber plans have uneven reach into local infrastructure, report finds
Eighty-eight per cent of respondents to the 2026 State CIO Survey rated cyberattacks against critical infrastructure as a high concern, according to a joint report from the National Association of State Chief Information Officers and General Dynamics Information Technology. The report also indicates that funding and shared support do not consistently extend to the local organisations operating essential services.
The remaining 12% of respondents expressed moderate concern, while 73% said critical-infrastructure protection formed part of a whole-of-state cybersecurity plan.
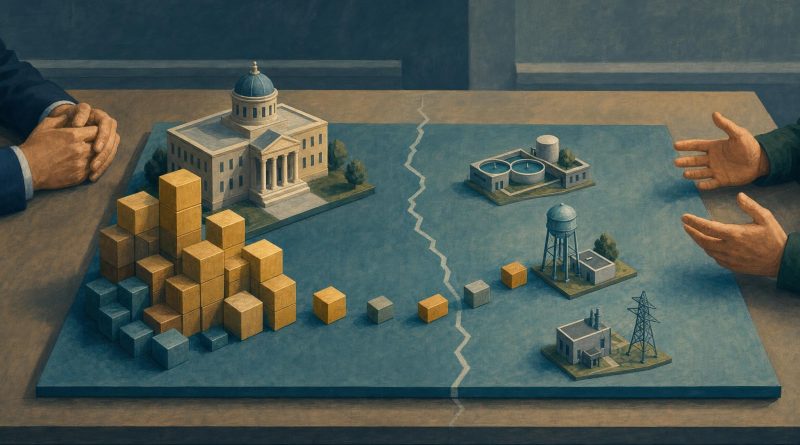
NASCIO announced the findings on 9 September in a report titled The Expanding Cyber Perimeter: States and Critical Infrastructure Protection. It describes a structural problem behind the plans: state chief information officers may be expected to coordinate broader resilience, yet essential services are frequently run by local governments, special districts or private organisations outside their direct jurisdiction.
That divide matters because the capacity to manage cyber risk varies across those organisations. The report identifies limited access to specialist staff, ageing technology, complex operational technology environments, remote-access exposure and fragmented authority as recurring problems. Responsibility for prevention and incident response can also remain unclear.
Funding narrows beyond state government
The budget figures show that state involvement is neither absent nor uniform. According to the report, 65% of state CIO budgets included critical-infrastructure cybersecurity funding for executive-branch agencies, and 33% covered all state agencies. Only 31% extended such funding to local governments and special districts, while 22% reported no dedicated funding.
Those categories are not mutually exclusive, so they cannot be combined into a single national funding total. They nevertheless illustrate the difference between financing security within state government and supporting the wider network of public bodies responsible for essential services.
This is not a finding that every state or locality lacks resources. Instead, the report describes uneven access to funding, expertise and central services. A state may fund cybersecurity for executive agencies without possessing the legal authority or sustained budget to provide equivalent support to a small utility or special district.
NASCIO and GDIT use New Jersey, Utah and Oregon as examples of whole-of-state or shared-service approaches. The report also points to legislative and emergency-coordination models in Kansas and Minnesota. Across these examples, assistance can include assessments, training, incident response, endpoint protection and shared security services, although participation and geographical reach vary.
The examples show that a whole-of-state label does not describe one operating model. Some programmes extend technical services, while others concentrate on coordination or legislation. The report does not establish that any model has been proven to prevent attacks or disruption, and figures associated with individual state programmes have not been independently verified for this article.
Operational technology complicates the boundary
The jurisdictional gap becomes more consequential where local operators depend on ageing or proprietary operational technology and supervisory control and data acquisition systems. Long equipment lifecycles, broad remote connectivity and incomplete asset visibility can make security work more difficult, particularly where an organisation has few specialist personnel.
None of those conditions shows that a system has been compromised. The report is a policy and capacity assessment, not an incident notice or vulnerability advisory, and it discloses no outage, data loss, service interruption or public-health impact.
Recent The Hack Academy reporting on water-system targeting has provided a more immediate backdrop to concern about locally operated infrastructure. The new report takes a broader view, focusing on governance and resources across sectors rather than documenting a particular campaign or attributing an incident.
Federal support remains uncertain
State chief information security officers interviewed for the report expressed concern about the future of Cybersecurity and Infrastructure Security Agency programmes, the Multi-State Information Sharing and Analysis Center and the State and Local Cybersecurity Grant Program.
The report presents those services and grants as important to the development of state and local capacity. It does not, however, independently establish the current operating or funding status of every programme. Concern that unstable federal support could stall state initiatives should therefore be distinguished from confirmation that all of those programmes have ended or been reduced.
To address the wider capacity gaps, NASCIO and GDIT recommend that states identify high-risk infrastructure, establish formal governance and incident responsibilities, expand shared services and develop sustainable state funding. The report also proposes encouraging or requiring basic cyber controls and considering mandatory incident reporting.
These are policy recommendations, not evidence of a single nationwide set of requirements. Their implementation would depend on the authority, legislation and resources available in each jurisdiction.
Useful findings with methodological limits
The report was produced jointly by NASCIO and GDIT, a government technology contractor, with Meredith Ward and Joshua Verville listed as its primary authors. It says the findings draw on the 2026 State CIO Survey, the 2026 NASCIO-Deloitte Cybersecurity Study and interviews with state CISOs.
The public report does not provide the complete survey methodology, including the respondent count, full question wording, field dates or response rate. It also contains an unresolved discrepancy between its prose and accompanying table over the proportion of respondents offering services to public electric, water and wastewater utilities. That percentage should not be treated as settled until NASCIO clarifies it.
Nor should the results be read as a quantitatively representative audit of every state, locality, special district or private infrastructure owner. The research principally reflects the perspectives of state CIOs and CISOs, and the extent of private-sector representation is unclear.
The research contains no Australian respondents, organisations or incidents, so it provides a governance comparison rather than evidence of equivalent Australian funding gaps. Australia is in Horizon 2 of its 2023 to 2030 Cyber Security Strategy, while covered critical-infrastructure entities have risk-management and incident-reporting obligations under the Security of Critical Infrastructure framework. The Australian Signals Directorate’s 2024 to 2025 threat report also identifies critical infrastructure as a target.
The next useful evidence will be the complete survey methodology, clarification of the conflicting utility-services statistic and independent confirmation of how far state support reaches local operators. Until then, the report provides a detailed account of uneven capacity, but not a nationwide audit of critical-infrastructure readiness.
Funding tables and jurisdiction boundaries describe organisational capacity, while networking fundamentals add technical context to the role of shared security services. Continue that enquiry with The Hack Academy’s online cybersecurity training programme, which lists cybersecurity fundamentals and networking among its subjects and combines self-paced learning with practical exercises alongside theory.
